Posts

BHIS CTF@Shmoocon 2019 - Blockchain Challenge

Image
I had the Blockchain Challenge, or whatever it was actually called, still kicking around even though Shmoocon and the Blackhills Infosec CTF has ended. I thought this was a neat challenge and I really wanted to figure this one out. Here's the challenge description: Thanks for joining our team on this one. We are so close to catching the infamous hacktivist known as "gh0st Plague". We were informed that he is planning another DDoS attack against a major financial institution. gh0st Plague recruits various botnet owners from around the net and always pays in Bitcoin. We believe that the following Bitcoin address is one of gh0st Plague's wallets. Knowing where and when gP is making payments should help us catch him but we need some solid evidence. This is where you come in. With your expertise in Blockchain analysis it shouldn't be too hard for you to determine if he let his ego get to him and left any clues behind. Good luck! 3AHnpGWb1EUSYKZUbgxfAkzFfmJeKLL3hH ...

Al Capwn: Evlz CTF 20190202-20190203

Image
I recently heard of the Evlz CTF from a reddit post in /r/securityCTF by u/coffee-loop. The CTF is put on by Al Capwn, a collaboration of Indian college CTF players with members from eavesdroppers, UPES, and Amrita University.  Holy macaroni did this competition blow me away! There were so many quality challenges I can't believe it was limited to less than 48 hours. I only had about 6 hours between Saturday and Sunday to put towards the challenges so I was only able to get a few of the "easy" ones. They had multiple challenges for each of the following categories: Sanity Misc Crypto Forensics Web Pwn Reverse I have write ups for the Sanity challenges as well as two of the Misc challenges. Let's get started: Sanity Check 1 1 point, simply enter the flag that was set for the ctf channel in the evlzctf slack workspace. evlz{I_pledge_to_play_fair_and_I_promise_to_not_attack_the_infrastructure}ctf Sanity Check 2 50 points. This challenge provi...

BHIS CTF@Shmoocon 2019 - Feeling Blue?

Image
I was lucky enough to score tickets to Shmoocon again and of course I was looking forward to working on a CTF while I was there. Black Hills Information Security  had organized a CTF to run at Shmoo which made me super happy as I have a lot of respect for them and was excited to see what they had in store for us players. Unfortunately, I had to work most of Friday and leave first thing Sunday morning. This left me with only a handful of hours on Saturday to compete as I balanced my time with other con activities. My coworker, Wole, joined the team and together we reached as high as 13th place in just a few hours. The final scoreboard was still hidden at the time of this writing, but I have a feeling we got knocked down a few spots. The CTF was powered by MetaCTF and the challenges were categorized as follows: Cryptography Reconnaissance Web Exploitation Reverse Engineering Forensics Other One challenge that I thought would make for a good blog post to write on the t...

Code Name: 2019 Stonecutters CTF

Image
A secret society, not unlike the illuminopi (did I spell that right?), is putting on a secret CTF that will run for all of 2019.  They will add challenges over the course of the year, some exist but are currently locked behind other challenges, and some will be retired as the solve rate reaches 100%. I have been given permission to write-up retired challenges if I scrub all of the CTF's identifying information. So that I can refer to this event, I've code-named it: the 2019 Stonecutters CTF. The 2019 Stonecutters CTF In addition to what I have already shared, I can tell you is that this a Jeopardy style CTF, when challenges are solved the point value decreases, and there are a lot of very high-level competitors playing...like 100 of them, so I don't expect to score a lot of points. Please feel free to check back every now and again for updates or watch the following twitter feeds for newly added write-ups: @strupo_ @TeamWTG Thanks, -strupo_ Challenge Wri...

Code Name: Treehouse of Horror CTF

Image
A friend of mine asked me if I wanted to participate, on the sly, in an internal CTF that he put together for his employer. My score wouldn't be shown, and for all intents and purposes I did not compete. I figured I'd give it a code name incase I need to refer to this event. Let's call it the Treehouse of Horror CTF. The Treehouse of Horror CTF! The scoreboard appeared to be similar to the one used at the Defcon 26 IoT CTF, however this one was organized by challenge which made things nice for tracking your own progress versus one huge board of challenges.  I think this is called Jeopardy style. There were some odd moments at times because different challenge groups shared a target, so you had to identify which flag went with which challenge. Really not that big of a deal and I actually really enjoyed the format rather than just a single submit field like at derby or Eversec's CTF as it helped me track my progress with ease. The challenges were: FreePBX Re...

SANS 2015 Shmoo Challenge - Better late than never!

Image
I'm patiently waiting for the SANS holiday challenge and thought I'd fill in the gap by revisiting my SANS 2015 Shmoo Challenge submission. Better late than never, right? Back in 2015, I competed in SANS 2015 Shmoo Challenge and was one of the first 10 participants who successfully completed the challenge. By doing so, I won this fancy NetWars T-Shirt: Fancy NetWars T-Shirt Normally these shirts are reserved for NetWars winners, so if you see someone wearing it, go talk to them - they did something cool! Sans and Counterhack put on high production value infosec challenges each year, and winners often get prizes such as training, NetWars access, rare shirts, etc...and anyone can compete for free. The best part about these challenges is that they maintain all of them so anyone can go back, as far as 2011, and still complete them which is just awesome! Okay - Let's get into it The end goal is to find the "phrase that pays" and send it in an emai...

2018 BSidesRDU CTF

Image
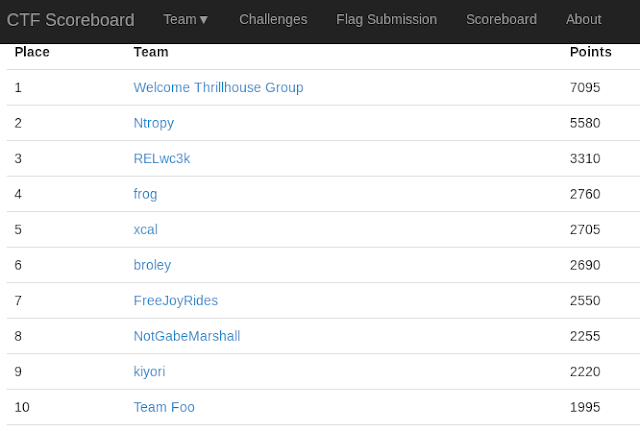
Winner! Winner! Welcome Thrillhouse Group took first place at the 2018 BSidesRDU CTF by that was put on by Eversec CTF . BSidesRDU Final Score Board. Team Ntropy was in the lead for most of the day and put up a really good fight, but WTG was able to pull ahead in the last few hours and hold first place till the end.  Our prize for taking first place was a copy of Clear and Present Danger by Tom Clancy:   Clear and Present Danger. However this is no ordinary edition!  This copy contains what appears to be a silk-screened or possibly etched BSidesRDU 2018 flask. BSidesRDU Flask. The team didn't really have time to put together any write-ups for this event. We were just too busy trying to overtake Ntropy the whole day. However, I did make some mental notes on the challenge involving the libssh vulnerability CVE-2018-10933, and still have some spool files from using metasploit so I'll talk about that briefly. [1] nmap indicated libss...